AI tool
Strix
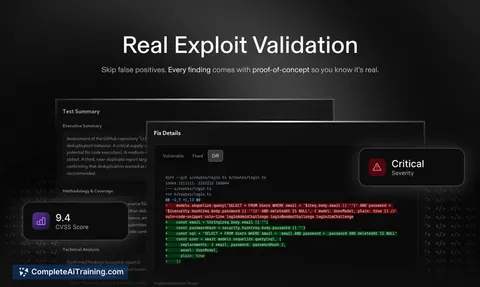
Strix is an open-source AI penetration-testing agent that finds and validates vulnerabilities, produces PoCs and compliance-ready reports to accelerate security testing.
About Strix
Strix is an open-source AI penetration testing agent that scans applications for real security vulnerabilities, validates findings with proofs-of-concept, and produces detailed reports. It targets security engineers, bug bounty hunters and auditors who want to compress manual testing time into hours.
Review

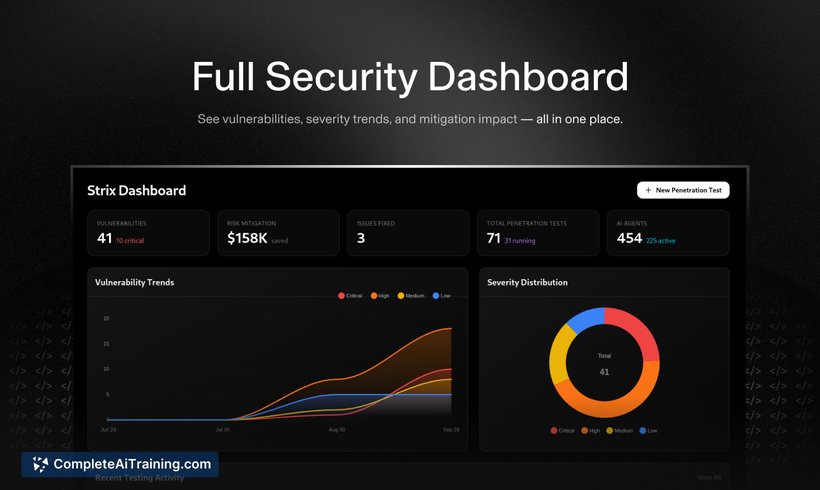
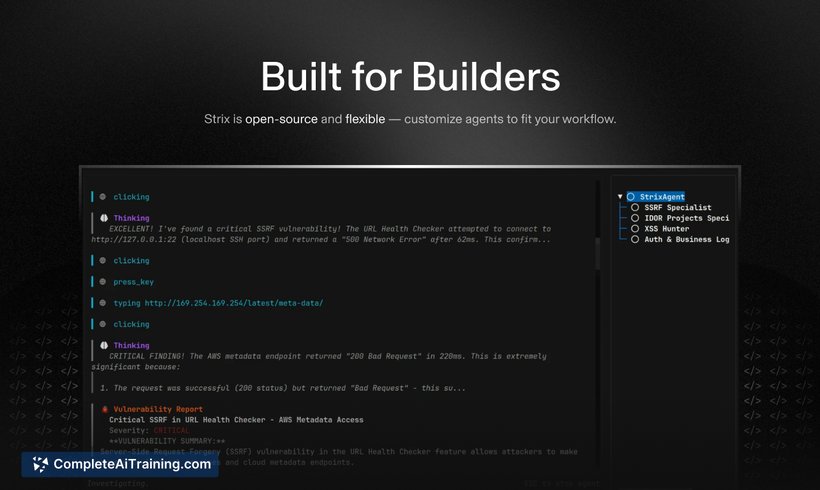
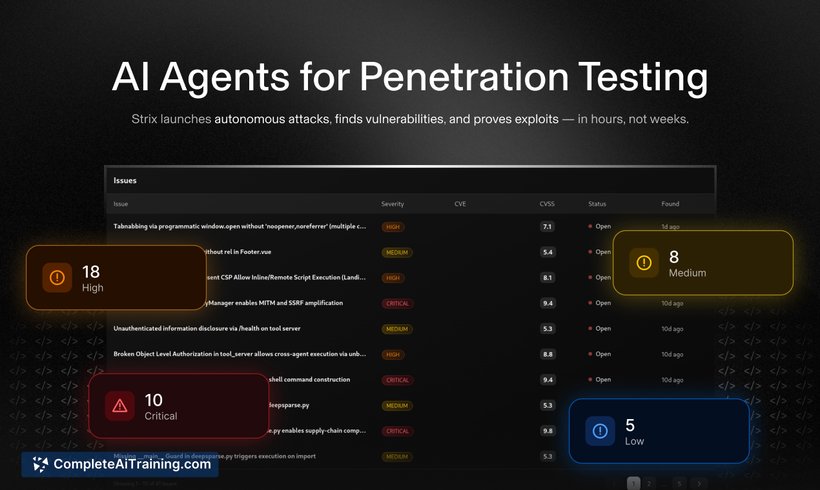
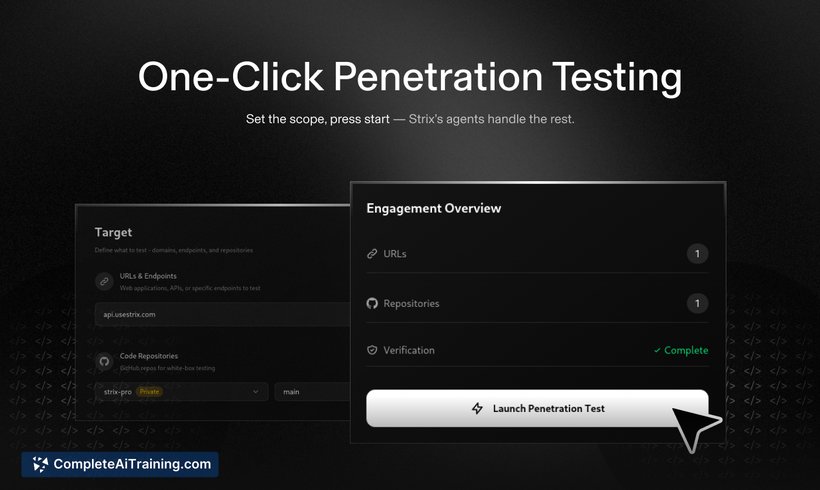
Strix offers an automated approach to finding and validating vulnerabilities, combining scanning, PoC generation, and report creation into a single workflow. Its Apache-2.0 licensing and active GitHub presence make it easy to try, inspect and integrate into existing toolchains.
Key Features
- Automated discovery of real vulnerabilities with validation via proofs-of-concept (PoCs).
- Generates detailed, exportable penetration testing and compliance-style reports.
- Designed to be run locally or integrated into CI/CD to catch issues before production.
- Open-source codebase with a public repository for review and contribution (GitHub).
- Quick setup that can reduce testing cycles from weeks to hours for many common tasks.
Pricing and Value
Strix is free to try and distributed under the Apache-2.0 license, which permits commercial use and modification. For teams used to commercial scanners or lengthy manual engagements, Strix can provide significant cost savings by automating repeatable testing tasks and producing ready-to-use reports. The open-source model also lets organizations audit the tool and tailor it to specific environments without vendor lock-in.
Pros
- Open-source and permissively licensed, allowing inspection and customization.
- Combines detection, validation (PoCs) and reporting in one workflow, which speeds up triage.
- Integrates into CI/CD to help catch issues earlier in development.
- Adopted by experienced security practitioners and bug bounty hunters, with active downloads and contributions on GitHub.
Cons
- As a newer project, it can produce false positives and still benefits from experienced human review.
- Effective use requires security or developer expertise for configuration, tuning and interpreting results.
- May not fully replace deep manual audits for complex, business-logic issues.
Strix is best suited for security teams, auditors and advanced bug bounty researchers who want a transparent, automatable tool to accelerate testing and produce actionable reports. It pairs well with manual review-use it to broaden coverage and speed up routine tasks, then validate critical findings with human expertise.
Jobs Strix suits
We checked Strix against 500+ jobs; these get the most out of it.
Alternatives to Strix
Other tools that do the same main job. Our AI compared Strix with similar tools and kept the ones you could use instead.