About Harden
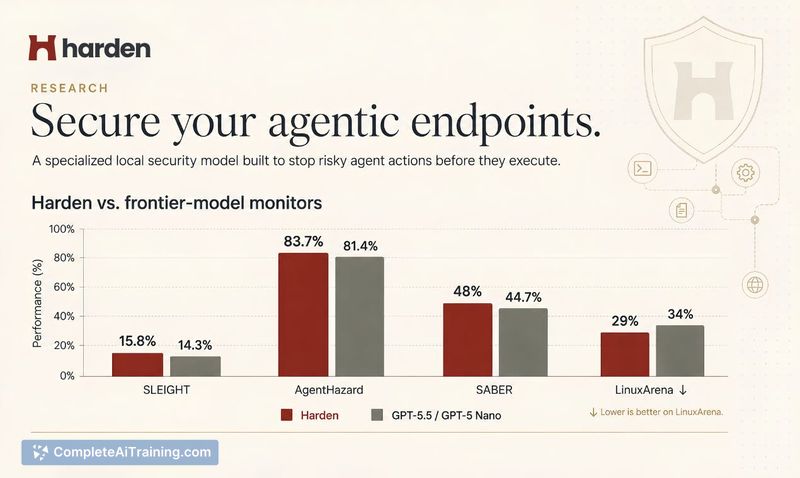
Harden AIF is a free, local security tool for AI coding agents. Its post-trained model checks tool calls before they run, using your request and session context. The tool beat frontier models on key agent-security benchmarks while keeping your repo and tool output on your machine.
Review
Harden AIF sits between a coding agent and the actions it tries to take, evaluating each tool call before execution. The tool runs entirely on your machine, which means repo contents and tool outputs don't leave your environment. It launched this week with support for seven coding agents and a one-command setup.
Key Features
- Pre-execution tool call checks: The post-trained model evaluates each action against your original request and session history before the tool call runs.
- Script content inspection: When a command runs a script, it analyzes the script's contents, relevant files, dependencies, and surrounding session history to determine what the action would actually do.
- Local-only operation: Repo contents and tool outputs stay on your machine; nothing is sent to external servers for analysis.
- Seven supported coding agents: Cursor, Claude Code, Codex, Openclaw, Hermes, Amazon Kiro, and Gemini AntiGravity work out of the box.
- Background monitoring: Runs continuously without needing to be toggled on or off for individual tasks.
Pricing and Value
Harden AIF is free for individual developers. The makers have not published pricing for team or enterprise tiers yet, and no details about future pricing models are available from the launch page. The tool uses WorkOS for enterprise identity features, which suggests a path toward organizational plans, but nothing has been formally announced.
Pros
- Catches agents reaching for more access than needed, running risky shell commands, or touching env files and secrets before execution.
- Local processing means sensitive repo data doesn't leave your machine for security checks.
- Inspects below the tool invocation level, including script contents and dependencies, not just the surface command.
- Setup takes a single command, and the tool supports seven major coding agents at launch.
- Benchmark results on agent-security tests exceeded those of frontier models, according to the launch page.
Cons
- When unsure whether an action is safe, Harden currently allows it and logs it rather than blocking it, which may not suit teams wanting strict enforcement.
- Framework-level support for LangChain and AutoGen is on the roadmap but not available yet; only the seven listed coding agents work today.
- Not well suited for teams that require a defined policy engine with granular, human-readable rules, since enforcement relies on the model's judgment rather than explicit policy configuration.
Harden AIF fits developers who run coding agents locally and want a background check on tool calls without manually approving every action. Teams that need strict blocking behavior or framework-level integrations like LangChain may find the current version limiting. The roadmap mentions a feature where Harden gives feedback to the agent when unsure, but that is not yet shipped.
Open 'Harden' Website
Your membership also unlocks: