AI agent for penetration testers
Attack Path Chaining Agent
Proven attack chains that show the real risk of combined findings
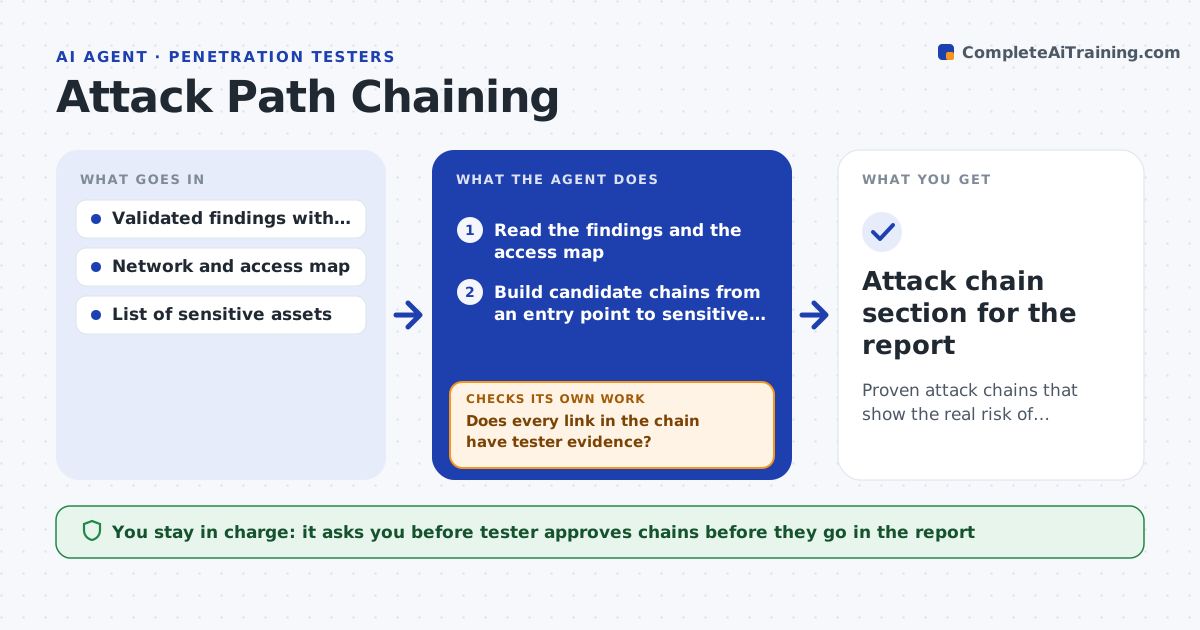
What it does
Low-severity findings are often reported alone when together they form a serious path to something important. This agent reads the validated findings and the network map and tests which combinations could lead from an entry point to a sensitive asset. For each chain, it checks every link against the tester's evidence. If one link has no proof, it drops that chain or marks the link as unproven. Chains with a full proven path are ranked by what they reach. The tester approves the chains for the report. Edge case: a weak password policy and an exposed file share connect only if the share is reachable from the user network, so the agent checks reachability first.
How it works
Follow the arrows from top to bottom. The orange dashed arrow is the loop: when a check fails, the agent goes back and tries again.
Read the steps as a list
- Findings are validated
- Read the findings and the access map
- Build candidate chains from an entry point to sensitive assets
- Rank candidates by the asset they reach
- Does every link in the chain have tester evidence?If not: mark the link unproven and try other candidate chains. Back to step 2.
- Is each step reachable from the previous one?If not: drop the chain or mark the break. Back to step 2.
- Describe each valid chain and its combined severity
- Tester approves the chains for the reportThe agent waits here for your OK.
- Attack chain section for the report
How it decides
A chain is valid only when each link has evidence and each step is reachable from the one before it.
- Accept a link only with evidence
- Check reachability between each pair of steps
- Rate the chain by the most sensitive asset reached
- List unproven chains separately as possible
Make it yours
Every agent is a starting point. You choose these settings for your own situation.
- Sensitive asset list
- Severity combination rules
- Minimum evidence per link
- Report format
What keeps you in control
It always asks you first
- Tester approves chains before they go in the report
Hard limits
- Never claims a chain without proof
- Never runs tests itself
It stops when
- Done: valid chains are listed and approved
- Stop: there are fewer than two validated findings
Set it up
We guide you through the set-up, step by step
Members get the full set-up guide for this agent. No technical skills needed: you copy, paste and upload.
- One set of instructions to paste into your AI, with the clicks for ChatGPT, Claude, Microsoft 365 Copilot, Gemini and Grok
- The agent then walks you through connecting your own data, one source at a time
- A downloadable copy with the flow chart, the rules and the full guide