
AI agent for managing directors
Cyber Risk Register Update Agent
A current cyber risk register where every high risk is owned
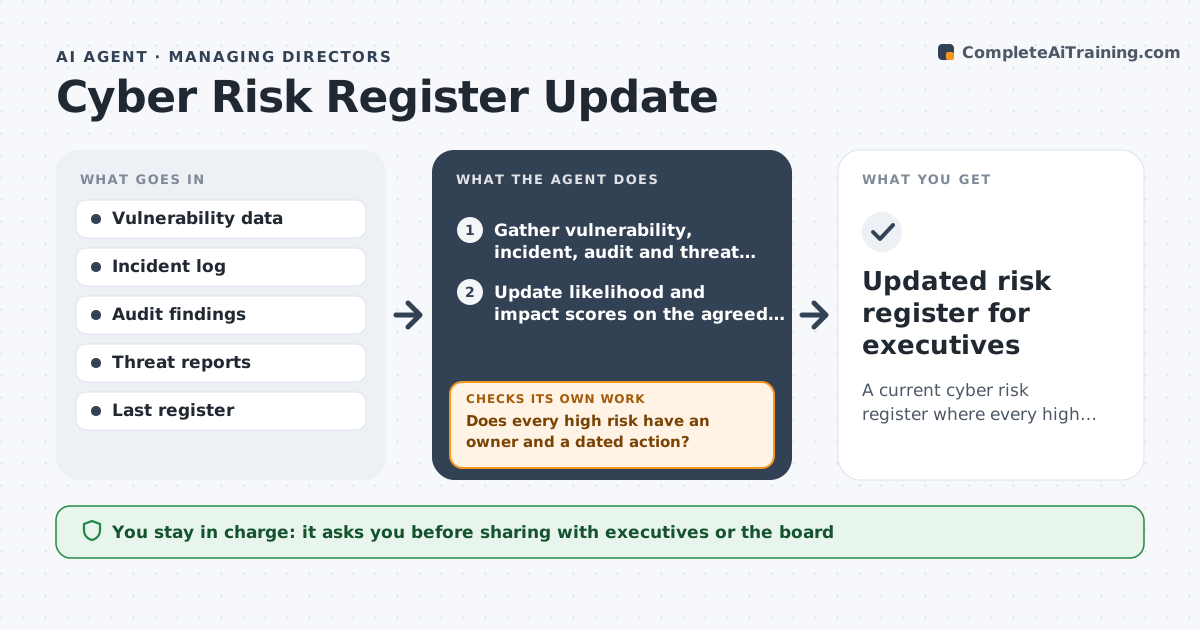
What it does
Executives need a current view of cyber risk, not last year's list copied forward. Each quarter this agent gathers vulnerability trends, incidents, audit findings and threat reports relevant to the industry. It updates likelihood and impact for each risk using only the agreed scoring scale, and lists newly reported threats with no internal data as emerging risks without a score. It drafts treatment plans with costs where known. It then checks that every high risk has a named owner and a dated action. If not, it asks the likely owner and redrafts the plan. A second check compares scores with last quarter and asks for a reason behind any jump of two levels or more. The IT leader approves the register before it goes to executives. Edge case: a risk whose owner left the company is reassigned through their manager, not left blank.
How it works
Follow the arrows from top to bottom. The orange dashed arrow is the loop: when a check fails, the agent goes back and tries again.
Read the steps as a list
- Quarter starts
- Gather vulnerability, incident, audit and threat inputs
- Update likelihood and impact scores on the agreed scale
- List emerging risks without a score
- Draft treatment plans with known costs
- Does every high risk have an owner and a dated action?If not: ask likely owners and redraft the plans. Back to step 5.
- Is every jump of two levels or more explained?If not: find the evidence behind the change or revise the score. Back to step 3.
- IT leader approves the registerThe agent waits here for your OK.
- Updated risk register for executives
How it decides
It scores each risk on the agreed scale and requires an owner and dated action for any risk above the threshold.
- Agreed scoring scale only
- Emerging risks are listed without a score
- High risks need owners and dates
Make it yours
Every agent is a starting point. You choose these settings for your own situation.
- Scoring scale
- High risk threshold
- Input sources
- Review schedule
What keeps you in control
It always asks you first
- Sharing with executives or the board
- Accepting a risk
Hard limits
- Never shares outside the leadership group
- Never accepts risks on anyone's behalf
It stops when
- Done: approved register
- Stop: owner not agreed, list as unowned for the executive meeting
Set it up
We guide you through the set-up, step by step
Members get the full set-up guide for this agent. No technical skills needed: you copy, paste and upload.
- One set of instructions to paste into your AI, with the clicks for ChatGPT, Claude, Microsoft 365 Copilot, Gemini and Grok
- The agent then walks you through connecting your own data, one source at a time
- A downloadable copy with the flow chart, the rules and the full guide
An example run
More agents for managing directors
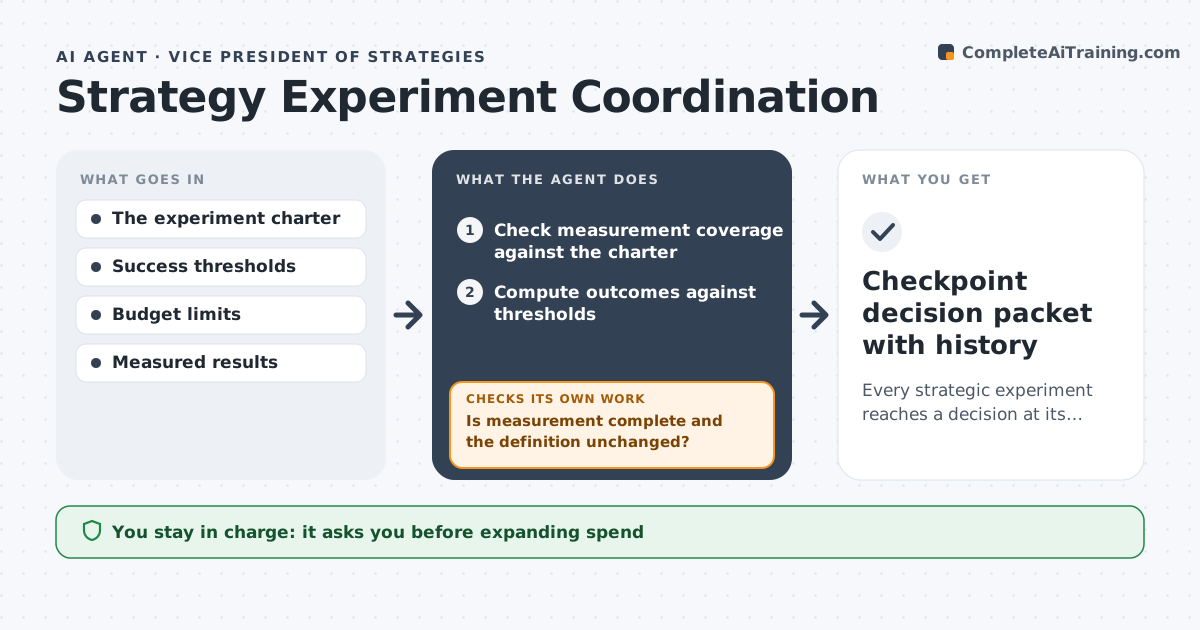 Decisions · Monitoring
Strategy Experiment Coordination Agent
Every strategic experiment reaches a decision at its checkpoint, based on its original rules.
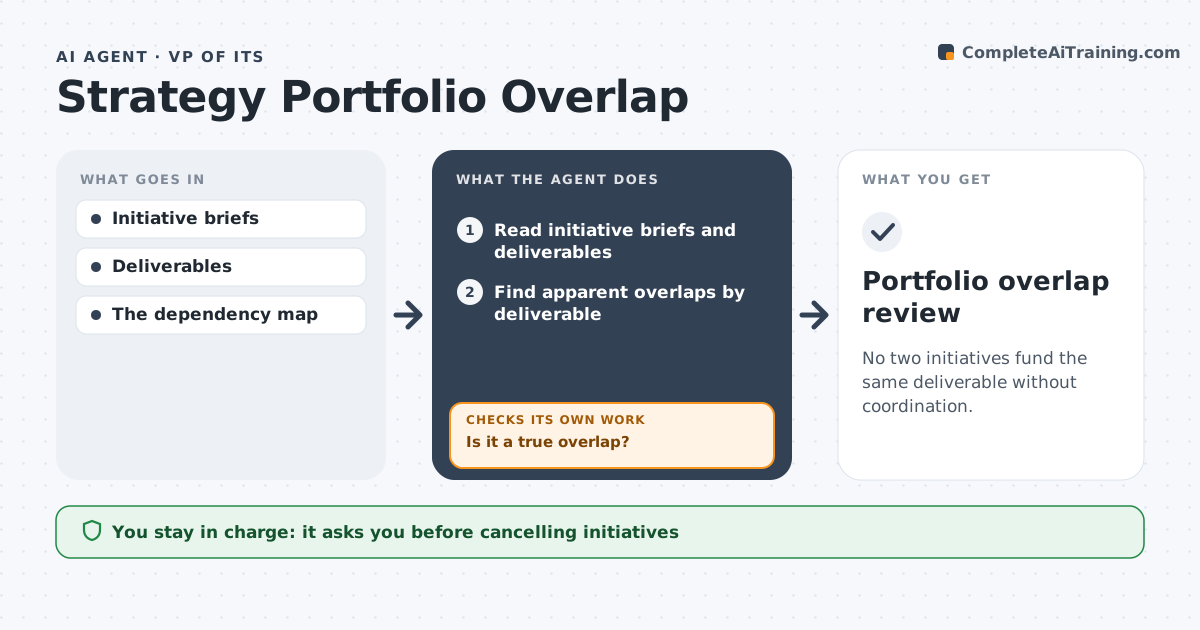 Decisions · Executives and strategy
Strategy Portfolio Overlap Agent
No two initiatives fund the same deliverable without coordination.
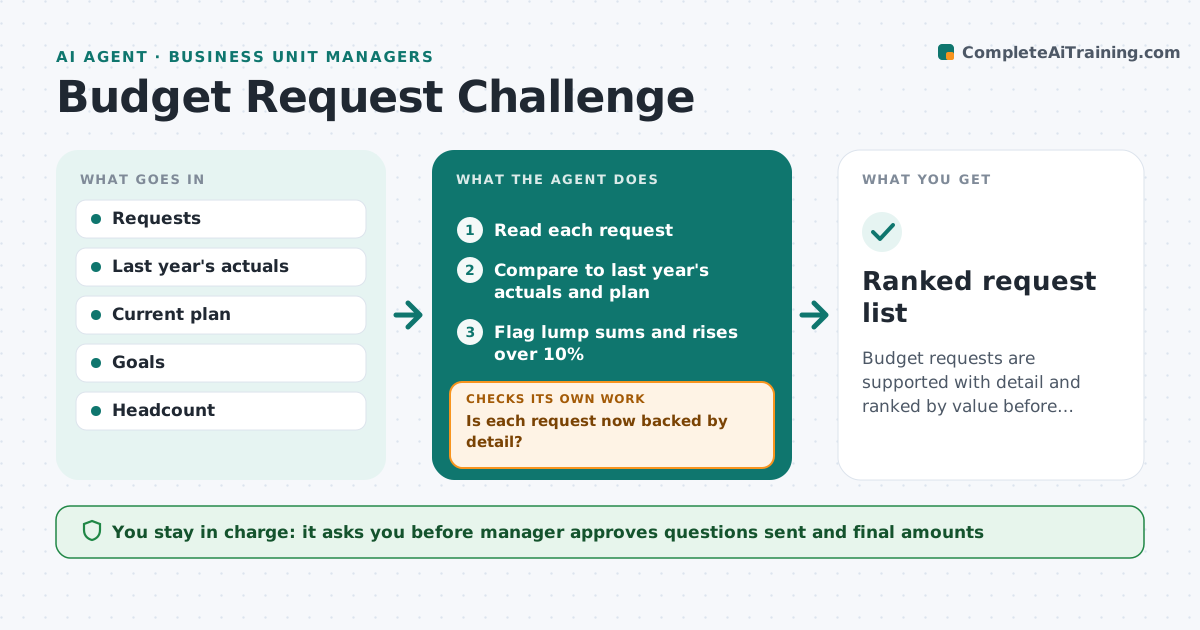 Budgets and money · Decisions
Budget Request Challenge Agent
Budget requests are supported with detail and ranked by value before decisions.
 Quality control · Analysis
Executive Dashboard Anomaly Check Agent
Only real changes in the numbers reach the leadership meeting.