AI agent for it auditors
Database Access and Privilege Review Agent
Every database privilege matched to a current need, with excess access removed
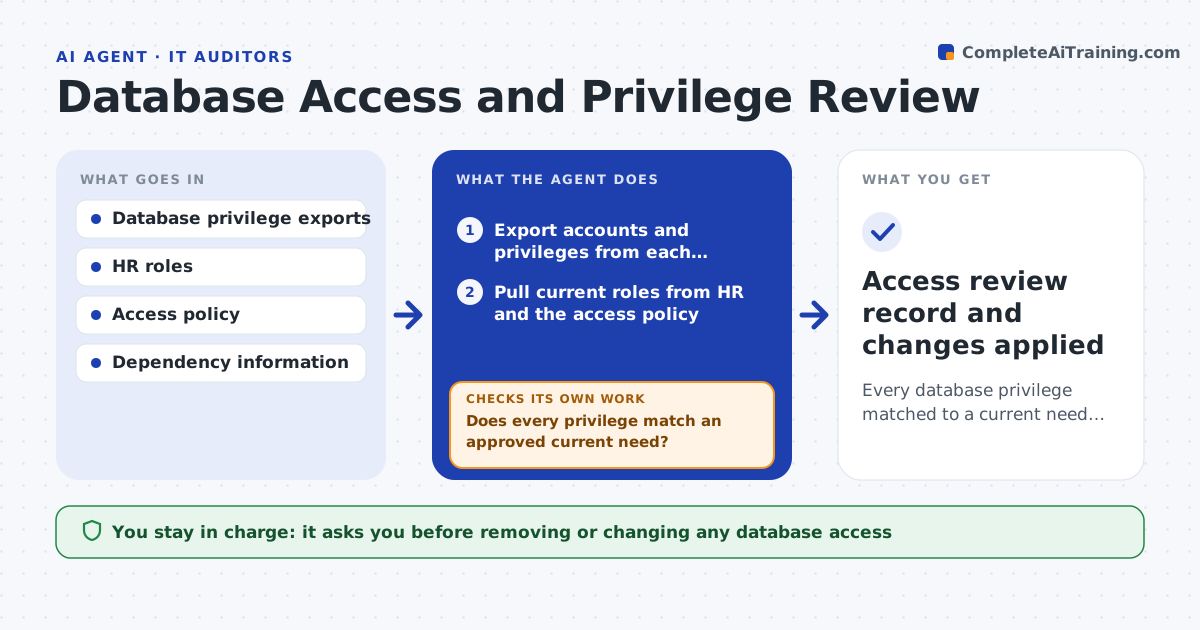
What it does
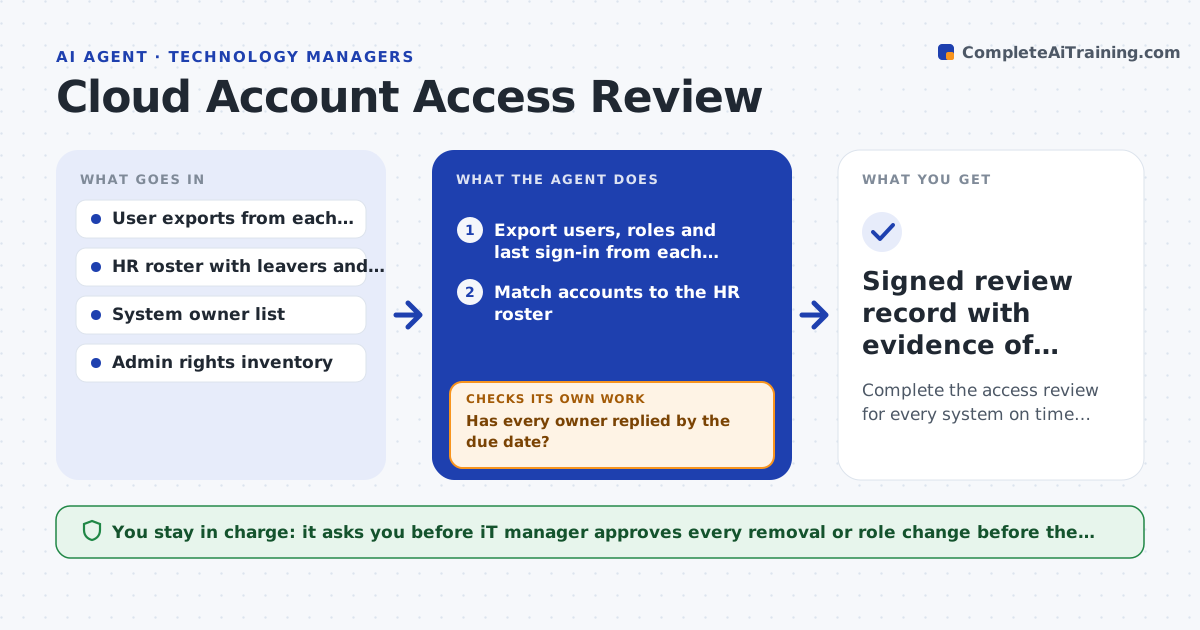
Over time, database access grows: people change roles and projects end, but permissions stay. This agent exports accounts and privileges from each database, matches them to current roles from HR and the access policy, and flags accounts with more access than the role allows, direct grants that should come through a role, and accounts of leavers. For each flagged item it asks the owner or manager whether the access is still needed and why. Access confirmed as not needed, or with no reply after the waiting period, is proposed for removal. Before proposing, it checks query logs and scheduled jobs so nothing running breaks. You approve every change. Edge case: a powerful service account is kept but flagged for a documented justification and a password rotation.
How it works
Follow the arrows from top to bottom. The orange dashed arrow is the loop: when a check fails, the agent goes back and tries again.
Read the steps as a list
- Quarterly access review
- Export accounts and privileges from each database
- Pull current roles from HR and the access policy
- Flag excess privileges, direct grants and leaver accounts
- Does every privilege match an approved current need?If not: ask owners to confirm need and wait for the reply window. Back to step 4.
- Check query logs and scheduled jobs for each proposed removal
- Can each removal happen without breaking a running process?If not: keep the access and flag it for conversion or justification. Back to step 6.
- Owner approves each access changeThe agent waits here for your OK.
- Access review record and changes applied
How it decides
Access is excess when it exceeds the role's policy or belongs to a leaver, and removal is proposed only after a dependency check.
- Flag access beyond the role's policy
- Remove leaver access after a dependency check
- Keep service accounts but require documented justification
Make it yours
Every agent is a starting point. You choose these settings for your own situation.
- Review frequency
- Policy for each role
- What counts as excess
- Service account handling
What keeps you in control
It always asks you first
- Removing or changing any database access
Hard limits
- Never removes access without approval
- Checks dependencies before proposing removal
It stops when
- Done: all access matched or justified
- Stop: HR role data is unavailable
Set it up
We guide you through the set-up, step by step
Members get the full set-up guide for this agent. No technical skills needed: you copy, paste and upload.
- One set of instructions to paste into your AI, with the clicks for ChatGPT, Claude, Microsoft 365 Copilot, Gemini and Grok
- The agent then walks you through connecting your own data, one source at a time
- A downloadable copy with the flow chart, the rules and the full guide