MCP server · Developer tools
TaskBounty Check MCP server
by eliottreich
Your AI can scan your GitHub Actions workflow files and explain CI maintenance issues in plain words.

TaskBounty Check is a small local helper that looks at the GitHub Actions workflow files in your project and points out maintenance problems. It is made for people who built an app with tools like Lovable, Bolt, Replit, Cursor, or v0 and now want to keep their automation tidy. It runs on your own machine and does not send your files anywhere.
What is an MCP server? The 30-second version
On its own, your AI can only chat with you. An MCP server is a small helper program that gives your AI a new skill or a connection to something useful. This one connects your AI to TaskBounty Check, a local scanner for your GitHub Actions workflow files. Once it is connected, you can ask your AI to scan your project and explain what it found, and the helper does the reading on your computer.
What this MCP server does
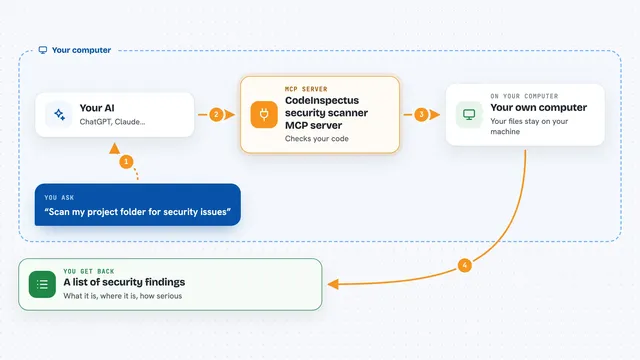
You ask your AI to check your project's workflow files. The AI uses this helper, which reads only the workflow files and update-automation config in your repo, right on your machine. The helper runs a fixed set of rules and finds things like actions pinned to a movable tag instead of a commit, or workflow permissions that are too broad. It hands the results back to your AI, which explains each finding in plain words and can write a fix plan as text. Nothing is uploaded and no files are changed for you.
 Click to zoom
What you can do with it
- Scan your repo's GitHub Actions workflow files for maintenance issues
- Get a plain-language explanation of any finding
- Receive a written fix plan you can apply yourself
- Check whether third-party actions are pinned to a commit
- Spot workflow token permissions that are too broad
- See if update automation like Dependabot or Renovate is missing
- Review flagged workflow patterns that deserve a closer look
Try asking your AI
- “Scan this repo and tell me what maintenance issues you find in my GitHub Actions workflows”
- “Explain this finding in simple words: third-party action pinned to a movable tag”
- “Write me a fix plan for the workflow permission issues you found”
- “Does my project have update automation set up for its dependencies?”
What it gives back to you
You get a short scan summary in the chat, a plain-language explanation for each finding, and a text fix plan you can read and apply yourself. Findings are grouped by category, with next steps. The helper never edits your files, so any change is up to you.
Before you start
What you need
- Node.js installed on your computer (the helper runs through npx)
- A project with GitHub Actions workflow files to scan
- An AI editor or app that supports MCP, like Cursor, Claude Code, or Codex
Good to know
It is a maintenance and hygiene check, not a full security audit, so it does not look for exposed secrets, login problems, payments, or runtime behavior.
Install it with your AI
Add TaskBounty Check MCP server to your AI, no technical skills needed
You don't install anything by hand. You copy one prompt, paste it into an AI that can work on your computer, and it checks, installs and connects the server for you, asking you when it needs something.
Sign in to get the install prompt
Members get a ready-made prompt that lets the Claude desktop app check TaskBounty Check MCP server, install it and connect it for them, step by step. You don't need any technical skills: you copy, paste and answer a few questions. Your connected AI can also find and install any of the 4,066 MCP servers here for you.
Who it's for
People who built an app with an AI builder and now want to keep their GitHub Actions and CI setup tidy, without deep DevOps knowledge.