MCP server · Security
mcp-shield security scanner
Let your AI check an MCP server or npm package for hidden dangers before you trust it.
mcp-shield is a safety checker for MCP servers. It looks inside a server's code and tells you if something looks sneaky, like sending your passwords somewhere or running hidden commands. It is handy if you like trying new AI add-ons but want to know they are safe first.
What is an MCP server? The 30-second version
On its own, your AI can only chat with you. An MCP server is a small helper program that gives your AI a new skill or a connection to an app. This one gives your AI the skill of checking other MCP servers for danger. So instead of you reading code yourself, you ask your AI and it does the checking for you.
What this MCP server does
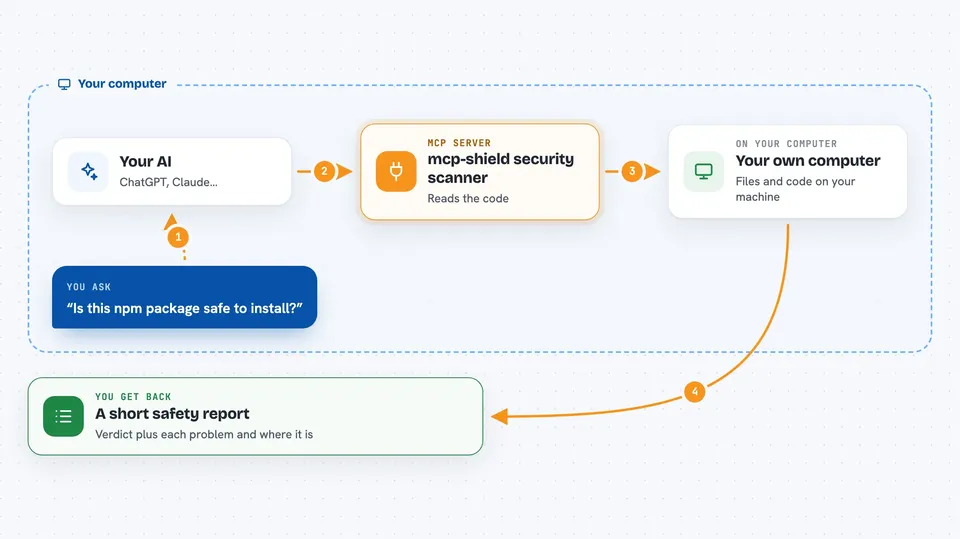
You ask your AI to look at a server or a package from npm. Your AI uses mcp-shield, which downloads or reads the code and looks for known bad patterns. It checks things like secret keys being sent over the internet, hidden commands, scrambled code, and sneaky instructions aimed at fooling an AI. Then it gives you a clear verdict with a list of what it found. It can also check how trustworthy a package is based on how old it is and how many people use it.
 Click to zoom
What you can do with it
- Scan an npm package before you install it
- Scan a folder on your computer where you cloned a server
- Check a piece of text for hidden prompt injection tricks
- Get a trust score and known issues for any npm package
- See a list of problems ranked by how serious they are
- Audit several MCP servers you already have installed
Try asking your AI
- “Scan the npm package some-sketchy-mcp-server before I install it”
- “Scan the MCP server I cloned at ~/projects/some-mcp”
- “Check this tool description for prompt injection: paste text here”
- “What is the trust score for popular-mcp-tool on npm?”
What it gives back to you
You get a short report in the chat with a verdict like SAFE, RISKY, or DANGEROUS. Under that, it lists each problem it found, the file and line number, and a short note about why it matters. For npm packages, you also get a small table with the package age, weekly downloads, and a trust score out of 100.
Before you start
What you need
- The Claude desktop app or another AI tool that supports MCP servers
- Node.js installed on your computer (the free program that runs these helpers)
- Internet access if you want to scan packages from npm
Good to know
It reads the code of servers and packages you point it at, so only scan things you are allowed to look at, and remember a clean scan is not a guarantee of safety.
Install it with your AI
Add mcp-shield security scanner to your AI, no technical skills needed
You don't install anything by hand. You copy one prompt, paste it into an AI that can work on your computer, and it checks, installs and connects the server for you, asking you when it needs something.
Sign in to get the install prompt
Members get a ready-made prompt that lets the Claude desktop app check mcp-shield security scanner, install it and connect it for them, step by step. You don't need any technical skills: you copy, paste and answer a few questions. Your connected AI can also find and install any of the 4,066 MCP servers here for you.
Who it's for
Anyone who likes trying new AI add-ons and wants a quick safety check before trusting them, especially people who are not coders.