MCP server · Security
SAST Security Scanner MCP server
by Skyrxin
Let your AI scan your code for security problems and help fix them.

This is a helper that gives your AI the ability to check your code for security weaknesses. It runs well known security scanners behind the scenes and hands the results back to your AI in plain language. It is handy for developers, testers and anyone who wants a quick safety check on a project without learning each scanner by hand.
What is an MCP server? The 30-second version
On its own, your AI can only chat with you. An MCP server is a small helper program that gives your AI a new skill or a connection to another tool. This one connects your AI to a set of security scanners, so when you ask it to check your code, it can actually run those scanners and read their results. You do not need to know how the scanners work. Your AI does the talking to the helper for you.
What this MCP server does
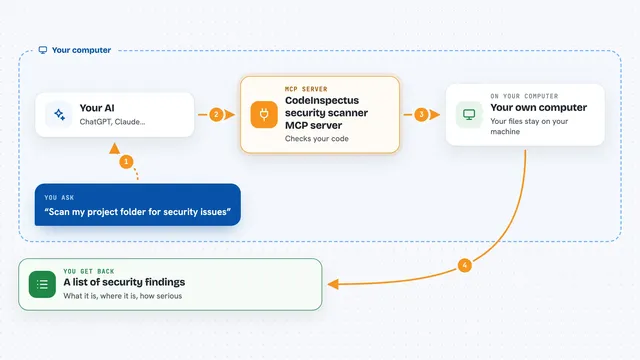
You point your AI at a folder of code and ask it to look for security issues. Your AI passes that request to this helper, which runs one or more security scanners on your files. The helper collects what the scanners found, tidies it up, and filters it by how serious each issue is. Then your AI shows you a list of problems with the file, the line, and a short explanation. It can also suggest fixes and, if you agree, apply them.
 Click to zoom
What you can do with it
- Scan a project folder for security vulnerabilities
- Run several scanners at once and combine the results
- Check your git history for leaked passwords and keys
- Filter findings by severity so you see the worst first
- Save a baseline and compare later scans to spot new issues
- Export results as a report or a SARIF file for your team's tools
- Generate a fix suggestion for a specific finding and apply it
Try asking your AI
- “Scan the project in my current folder for security problems and show me the most serious ones”
- “Run all available scanners on this codebase and give me a short summary”
- “Check my git history for any leaked API keys or passwords”
- “Compare this scan to the baseline called main and tell me what is new”
What it gives back to you
You get back a list of findings in the chat. Each one shows the file, the line, the kind of problem, and how serious it is. You can also ask for a summary report, a SARIF file, or a baseline comparison. If you ask for a fix, the AI can show you a suggested change and apply it to your files.
Before you start
What you need
- Python installed on your computer
- At least one security scanner installed (the full Docker image includes several)
- Docker if you want the all-in-one setup or the dynamic web scan
- A GitHub token or DefectDojo details only if you want to upload results there
Good to know
It reads your code and git history, and the apply_patch tool can change files on your disk, so review any suggested fix before you let it run.
Install it with your AI
Add SAST Security Scanner MCP server to your AI, no technical skills needed
You don't install anything by hand. You copy one prompt, paste it into an AI that can work on your computer, and it checks, installs and connects the server for you, asking you when it needs something.
Sign in to get the install prompt
Members get a ready-made prompt that lets the Claude desktop app check SAST Security Scanner MCP server, install it and connect it for them, step by step. You don't need any technical skills: you copy, paste and answer a few questions. Your connected AI can also find and install any of the 4,066 MCP servers here for you.
Who it's for
Developers, testers and small teams who want a quick security check on their code without learning each scanner by hand.