MCP server · Security
DocSentinel MCP server
by arthurpanhku
Let your AI review security documents and reports, then list risks, compliance gaps, and fixes.

DocSentinel is a security review helper for documents. You give it things like security questionnaires, design documents, or test reports, and it points out risks, missing compliance items, and suggested fixes. It is handy if you work in security, compliance, or software teams and want a first pass before a human reviews everything.
What is an MCP server? The 30-second version
On its own, your AI can only chat with you. An MCP server is a small helper program that gives your AI a new skill or a connection to another app or service. This one connects your AI to DocSentinel, a security assessment service, so your AI can send documents there and bring back the results. You ask in plain words, and the helper does the work in the background.
What this MCP server does
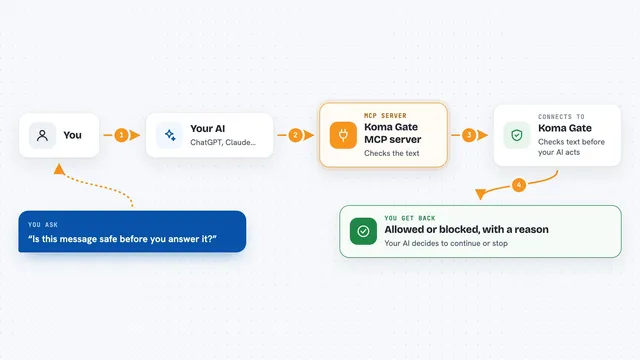
You ask your AI to review a document or a set of project files. Your AI passes the request to this helper, which talks to DocSentinel. DocSentinel reads the documents, compares them against policies and standards you have loaded, and runs its security checks. Then it sends back a structured report with risks, compliance gaps, and suggested fixes, and your AI shows that to you in the chat.
 Click to zoom
What you can do with it
- Review a security questionnaire and list the gaps
- Check a design document for security risks
- Triage a SAST or DAST report and rank the findings
- Compare a document against a framework like ISO 27001 or PCI DSS
- Suggest fixes for the issues it finds
- Track a project's readiness and control coverage
- Run a threat model check against your architecture documents
Try asking your AI
- “Review this security questionnaire and tell me what is missing”
- “Look at this design document and list the top security risks”
- “Check this test report against our policy and rank the issues”
- “What compliance gaps do you see in this document for ISO 27001”
What it gives back to you
You get back a structured report in the chat. It usually lists risk items with severity levels, compliance gaps against the frameworks you use, and suggested remediation steps. Some results also include readiness scores or evidence references so you can see where a finding came from.
Before you start
What you need
- A running DocSentinel service (local or cloud) that you can connect to
- An API key or access token for that service
- An LLM provider key (for example OpenAI, Anthropic, Qwen, DeepSeek, or a local Ollama setup)
Good to know
DocSentinel reads the documents you send it and can create or change assessment records, so avoid sending sensitive material unless you are allowed to, and always have a human review the findings before acting on them.
Install it with your AI
Add DocSentinel MCP server to your AI, no technical skills needed
You don't install anything by hand. You copy one prompt, paste it into an AI that can work on your computer, and it checks, installs and connects the server for you, asking you when it needs something.
Sign in to get the install prompt
Members get a ready-made prompt that lets the Claude desktop app check DocSentinel MCP server, install it and connect it for them, step by step. You don't need any technical skills: you copy, paste and answer a few questions. Your connected AI can also find and install any of the 4,066 MCP servers here for you.
Who it's for
Security analysts, compliance officers, and software teams who review documents and reports and want a fast first pass before human sign-off.