MCP server · Developer tools
Package Health MCP server
by orcsnren
Your AI can check if a package or GitHub project is still maintained before you add it to your project.
This is a small helper that lets your AI look up how healthy a software package is. It gives each package a score from 0 to 100, a letter grade from A to F, and a plain list of problems like "deprecated" or "no commits in a year". It is handy for anyone who installs open-source packages and wants to avoid ones nobody is taking care of.
What is an MCP server? The 30-second version
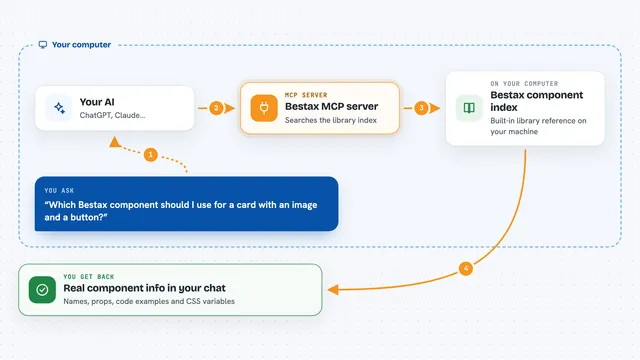
On its own, your AI can only chat with you. An MCP server is a small helper program that gives your AI a new skill or a connection to a service. This one connects your AI to package registries like npm and PyPI, and to GitHub. So when you ask about a package, your AI can actually go and check it instead of guessing from old training data.
What this MCP server does
You ask your AI something like "is this package still maintained?". Your AI passes the name to this helper. The helper then looks up release dates, commit activity, how many people maintain it, how fast issues get answered, download trends, a security score and the license. It adds all that up into one score and a short list of risks, and hands it back to your AI, which explains it to you in the chat.
What you can do with it
- Score a single npm or PyPI package and see its grade
- Scan a package.json or requirements.txt file and rank the riskiest dependencies first
- Check lock files to catch abandoned packages hiding deep in your dependency tree
- Compare two to five packages side by side before picking one
- Score any GitHub repository by owner and repo name
- Spot deprecated packages, archived projects, and packages with no recent releases
- Get a plain-language list of risks instead of just a number
Try asking your AI
- “Is the request package still maintained? Should I replace it?”
- “Scan this project's package.json and tell me which dependencies look abandoned”
- “Compare dayjs, date-fns and luxon before I pick a date library”
- “Check every package in requirements.txt and list the ones graded D or F”
What it gives back to you
You get a short summary line first, like "left-pad: 10/100 (F), likely abandoned or unsafe to adopt". Then a breakdown of each signal with its score and a short explanation, plus a bullet list of concrete risks. For a whole file, you get a count of packages scanned, how many got each grade, and the riskiest ones listed first.
Before you start
What you need
- Node.js 20 or later on your computer
- An MCP client like Claude Desktop, Claude Code, Cursor or VS Code
- Optional: a GitHub token (a kind of password for GitHub; you make one for free in your GitHub settings) to check many packages without hitting limits
Good to know
It only reads public information and does not change anything, but without a GitHub token it can only check a handful of packages per hour.
Install it with your AI
Add Package Health MCP server to your AI, no technical skills needed
You don't install anything by hand. You copy one prompt, paste it into an AI that can work on your computer, and it checks, installs and connects the server for you, asking you when it needs something.
Sign in to get the install prompt
Members get a ready-made prompt that lets the Claude desktop app check Package Health MCP server, install it and connect it for them, step by step. You don't need any technical skills: you copy, paste and answer a few questions. Your connected AI can also find and install any of the 4,609 MCP servers here for you.
Who it's for
Developers, engineering leads and anyone who installs open-source packages and wants to avoid abandoned ones.