

SpendShield MCP server
by felixpg13-glitchLets your AI ask permission before it spends money, and keeps a record of every attempt.
AI Library · 4,609 MCP servers
Lets your AI ask permission before it spends money, and keeps a record of every attempt.

Lets your AI record, review, and look up trust decisions for risky changes before they go live.

Check a live website for secret files like .git, .env, backups and source maps that anyone can read.
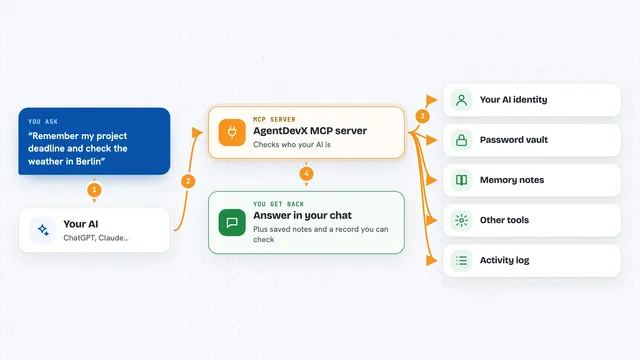
Give your AI a safe identity, a locked vault for passwords, and a memory that lasts between chats.

Your AI gets a strict bouncer between it and any outside tool, saying yes or no out loud.

Your AI checks risky actions first and gets back a risk score, red flags, and a go, caution, or stop call.
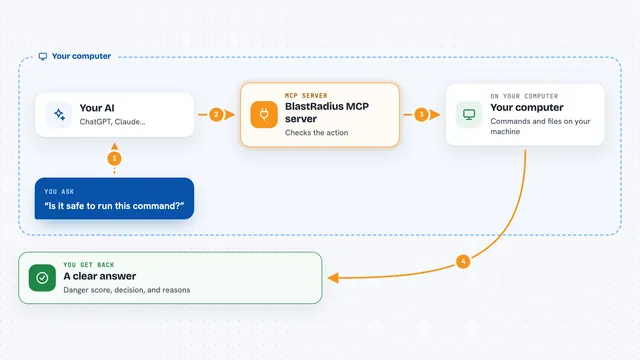
Check how dangerous an AI action is before it runs, hide secrets, and keep a tamper-proof record.
Check text for hidden tricks and sneaky characters before your AI acts on it.

Your AI can write, check and test safety rules for other AI agents, so those rules can't be talked around.

Your AI's risky actions get checked against your rules first: some go through, some wait for you, some are blocked.
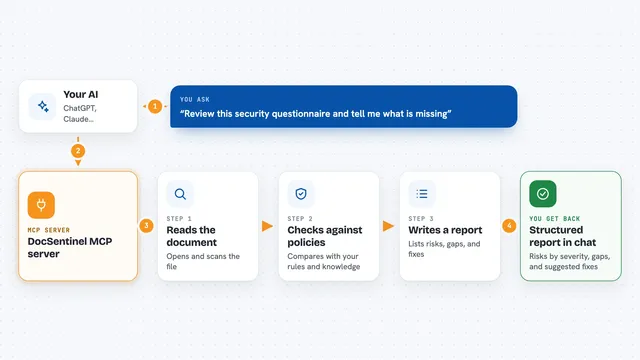
Lets your AI review security documents and reports, then list risks, compliance gaps, and fixes.

Ask your AI to scan a domain and get a scored security and privacy report with plain advice.

Adds a safety gate that checks and blocks risky AI tool calls before they run on your computer.

Lets your AI pause risky actions until a named person approves them.
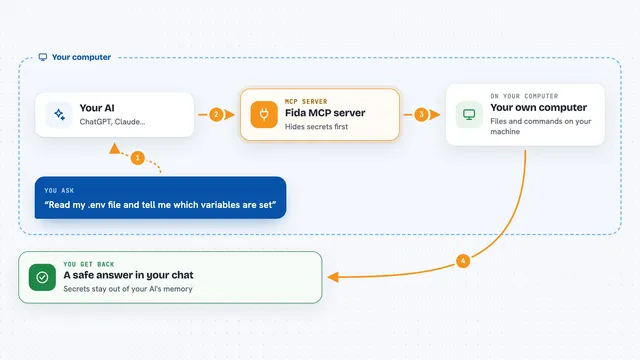
Keeps passwords and API keys out of your AI coding agent by hiding them before the AI sees them.
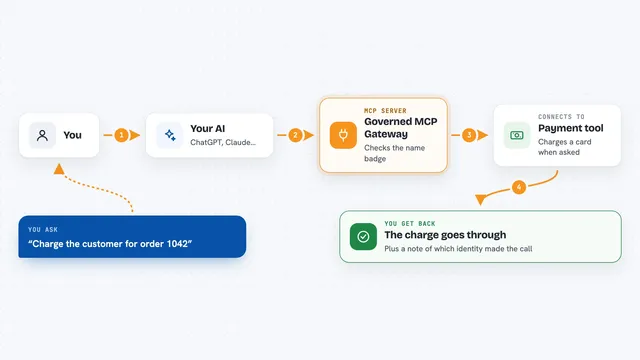
Adds a named identity to every AI tool call and keeps a list of which tools are allowed.

Let your AI fact-check claims, check its own answers, and screen risky computer actions before they happen.

Put one simple rules file between your AI and its tools, so risky actions get blocked or flagged before they happen.

Keep a tamper-proof record of every tool call your AI makes, so you can check what it really did.

Adds a safety layer between your AI and its tools, logging every action and blocking risky ones.
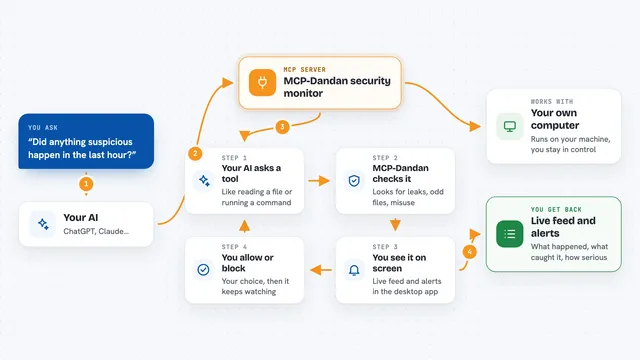
Watch your AI's tool calls in real time and block suspicious behavior before it causes harm.
Lets your AI check your MCP config files for risky settings and explain what it finds.

Let your AI keep a signed, checkable record of what it was allowed to do and what it actually did.

Lets your AI run security checks like SQL injection tests, network capture analysis and memory forensics for you.