

Assay MCP security
by Rul1anYour AI gets a strict bouncer between it and any outside tool, saying yes or no out loud.
AI Library · 4,066 MCP servers
Your AI gets a strict bouncer between it and any outside tool, saying yes or no out loud.

Your AI checks risky actions first and gets back a risk score, red flags, and a go, caution, or stop call.

Your AI can write, check and test safety rules for other AI agents, so those rules can't be talked around.

Your AI's risky actions get checked against your rules first: some go through, some wait for you, some are blocked.
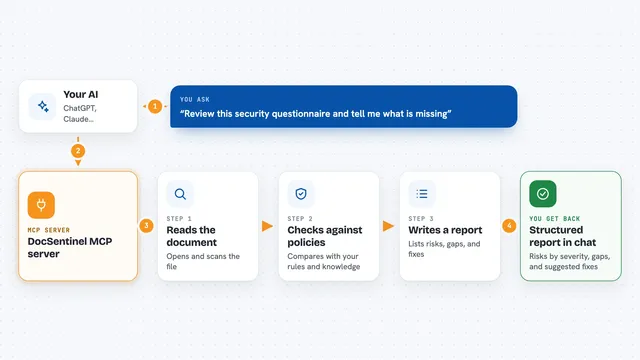
Lets your AI review security documents and reports, then list risks, compliance gaps, and fixes.

Ask your AI to scan a domain and get a scored security and privacy report with plain advice.

Adds a safety gate that checks and blocks risky AI tool calls before they run on your computer.

Lets your AI pause risky actions until a named person approves them.
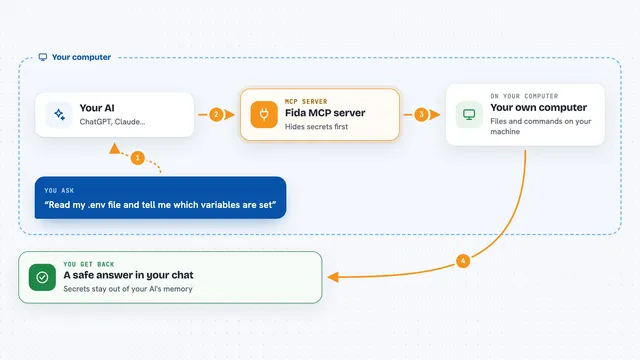
Keeps passwords and API keys out of your AI coding agent by hiding them before the AI sees them.
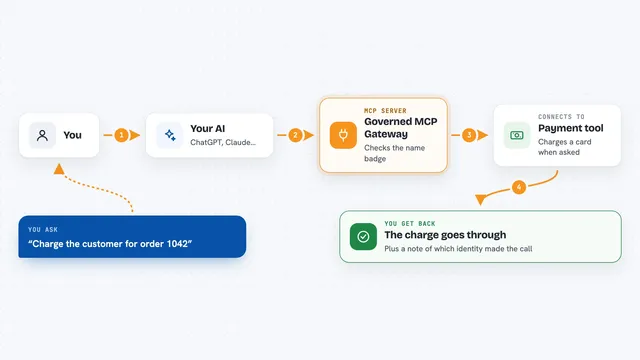
Adds a named identity to every AI tool call and keeps a list of which tools are allowed.

Let your AI fact-check claims, check its own answers, and screen risky computer actions before they happen.

Put one simple rules file between your AI and its tools, so risky actions get blocked or flagged before they happen.

Keep a tamper-proof record of every tool call your AI makes, so you can check what it really did.

Adds a safety layer between your AI and its tools, logging every action and blocking risky ones.
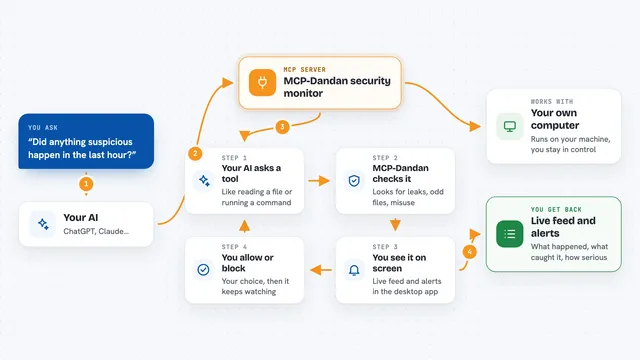
Watch your AI's tool calls in real time and block suspicious behavior before it causes harm.

Let your AI keep a signed, checkable record of what it was allowed to do and what it actually did.

Lets your AI run security checks like SQL injection tests, network capture analysis and memory forensics for you.

Your AI checks risky actions before doing them, and asks you first when something looks dangerous.
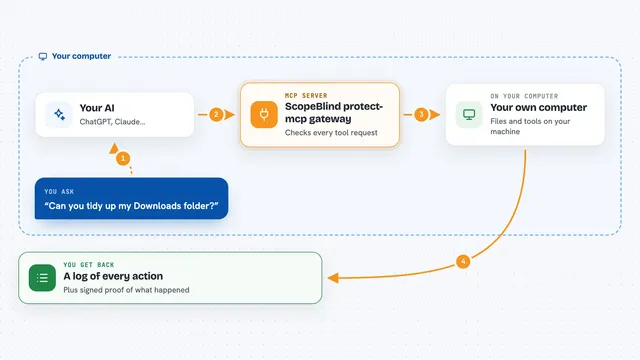
Watch and control what your AI's tools are allowed to do, with a log of every action.

Lets your AI check skill files and prompts for hidden security threats before you trust them.

Check and pin your AI skills and MCP servers so a tampered or poisoned tool never runs.
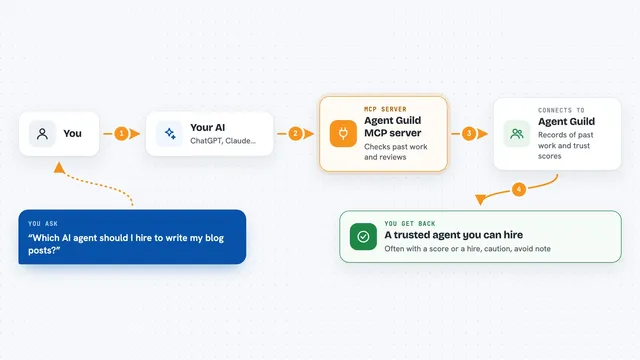
Lets your AI look up which other AI agents are trustworthy before it hands them a job.

Checks your AI's commands before they run and blocks dangerous ones like deleting files or reading passwords.

Lets your AI check any text for hidden prompt injection attacks before you trust it.