

HoneyLabs MCP server
by honeylabshqAsk your AI whether an IP is a known scanner, what CVEs it probes, and who is attacking what.
SecurityNo install
AI Library · 4,066 MCP servers
Ask your AI whether an IP is a known scanner, what CVEs it probes, and who is attacking what.

Add a safety layer that checks and blocks risky tool calls before your AI can run them.

Your AI can scan a project for leaked passwords, risky commands and unsafe tool descriptions.

Lets your AI scan code for old-style crypto that quantum computers could break, and suggest safer replacements.

Lets your AI send and test web requests at a low level, for security checks and fuzzing.

Checks every tool call your AI makes and blocks, warns or holds it before it reaches your apps.

Let your AI use your passwords and API keys without ever seeing the actual values.

Lets your AI ask permission before it spends money, and keeps a record of every attempt.

Lets your AI record, review, and look up trust decisions for risky changes before they go live.

Check a live website for secret files like .git, .env, backups and source maps that anyone can read.
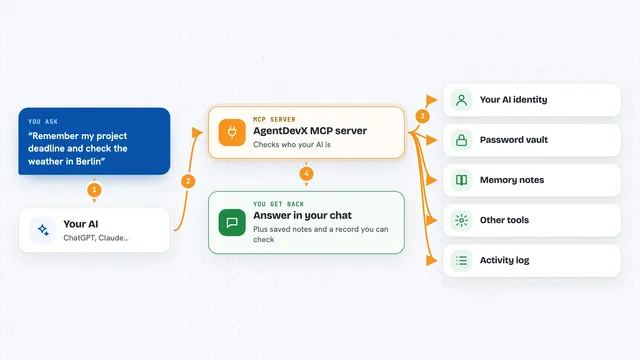
Give your AI a safe identity, a locked vault for passwords, and a memory that lasts between chats.

Your AI gets a strict bouncer between it and any outside tool, saying yes or no out loud.

Your AI checks risky actions first and gets back a risk score, red flags, and a go, caution, or stop call.

Your AI can write, check and test safety rules for other AI agents, so those rules can't be talked around.

Your AI's risky actions get checked against your rules first: some go through, some wait for you, some are blocked.

Ask your AI to scan a domain and get a scored security and privacy report with plain advice.

Adds a safety gate that checks and blocks risky AI tool calls before they run on your computer.

Lets your AI pause risky actions until a named person approves them.
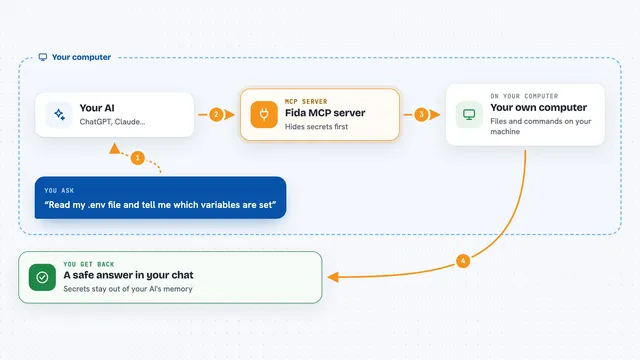
Keeps passwords and API keys out of your AI coding agent by hiding them before the AI sees them.
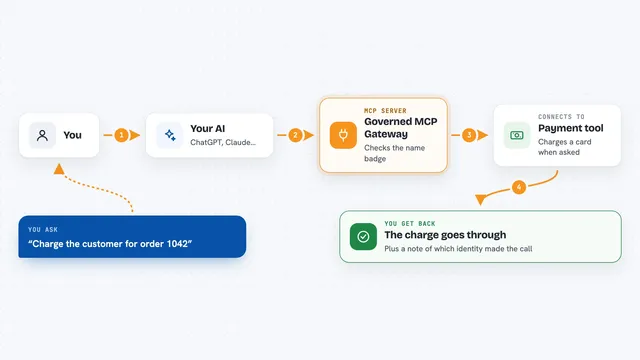
Adds a named identity to every AI tool call and keeps a list of which tools are allowed.

Let your AI fact-check claims, check its own answers, and screen risky computer actions before they happen.

Put one simple rules file between your AI and its tools, so risky actions get blocked or flagged before they happen.

Keep a tamper-proof record of every tool call your AI makes, so you can check what it really did.

Adds a safety layer between your AI and its tools, logging every action and blocking risky ones.