

MCP Blast-Radius Auditor
by aos-standardCheck what an MCP server can actually touch, like files, network, and commands, before you trust it.
AI Library · 4,066 MCP servers
Check what an MCP server can actually touch, like files, network, and commands, before you trust it.

Keep your passwords and API keys in an encrypted vault so your AI can use them without ever seeing them.

Let your AI call services like Slack or GitHub without ever seeing the real passwords or keys.

Turns your AI coding rules into real guardrails that can block bad actions and log what happened.

Share encrypted, self-destructing secret links from your AI without the secret ever passing through the chat.

Ask your AI to search Panther security logs, check alerts, and review detections in plain English.

Lets your AI scan your code for dead code, security problems, and quality issues before you merge.

Your AI can strip emails, phone numbers, IDs and card numbers out of text before it sends that text anywhere.

Lets your AI look up, create, and organize passwords and secure notes in your Bitwarden or Vaultwarden vault.

Lets your AI pull apart closed-source Solana smart contracts and hand you back their inner structure.

Let your AI use stored API keys and passwords inside commands without ever seeing the actual secret.

Your AI checks each request against your company's code of conduct and refuses the ones that are not allowed.

Lets your AI map how your code calls itself, spot security risks, and check licenses across repos.
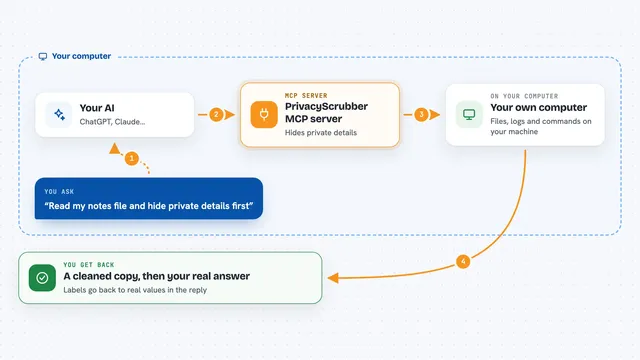
Your AI can read your files and logs with emails, keys, and passwords hidden first.
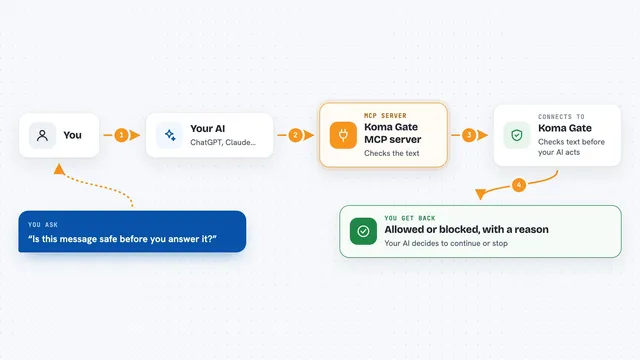
Lets your AI check if untrusted text is safe and in scope before it acts on it.

Lets your AI scan a code folder and score how safe and production-ready it looks.

Lets your AI check links, files, IP addresses and domains for signs of malware or scams.

Your AI checks its own code changes for security and risky edits before saving them, and tells you what it fixed.

Let your AI check your AWS account for security holes and explain what an attacker could reach.

Lets your AI read your code and answer questions about how data moves through it.

Ask your AI about Microsoft's monthly security updates, CVEs, KB fixes and what to patch first.

Ask your AI to read a network capture file and explain what happened inside it.

Let your AI manage NSX firewall rules, security groups, tags, and trace packets for you.
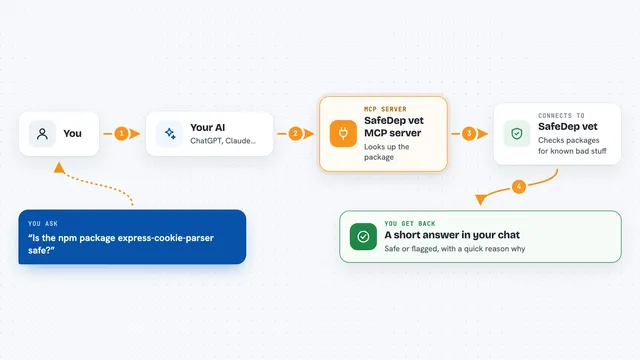
Lets your AI check npm and PyPI packages for known malware and vulnerabilities before you install them.