

DocSentinel MCP server
by arthurpanhkuLet your AI review security documents and reports, then list risks, compliance gaps, and fixes.
AI Library · 4,066 MCP servers
Let your AI review security documents and reports, then list risks, compliance gaps, and fixes.

Let your AI check an MCP server or npm package for hidden dangers before you trust it.

Let your AI check, audit, fix and write smart contracts for Ethereum, Solana and other chains.

Records what your AI agent really does, writes a tight permission policy from it, and checks every action against it.

Ask your AI to check a phone number, link, text, email, document or QR code for scam signs.

Lets your AI check a name against U.S. exclusion and debarment lists and hand you a signed receipt.

Lets your AI run commands that need passwords or keys, without ever seeing the secret values.

Check what changed in an MCP server, skill or plugin before you trust or update it.

Lets your AI check any web link for redirects, fake brands, domain age, SSL and other risk signals.

Adds a security guard between your AI and its tools, so risky actions get blocked or need your approval.

Gives your AI safety checks: it spots harmful text, hidden passwords, tricky prompts, and risky links.

Stops your AI agent before it runs a dangerous command, and checks the tools it uses for tampering.
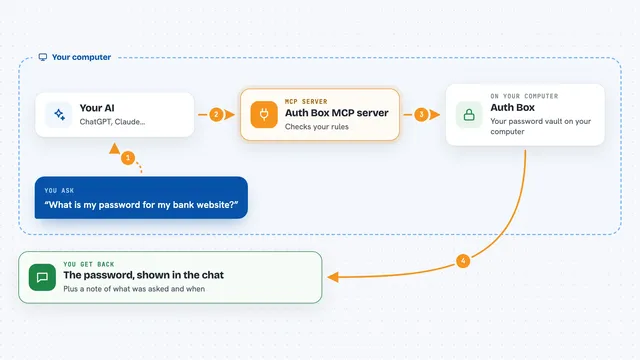
Let your AI look up and use your saved passwords and API keys, only for the things you allow.

Turn your AI agents' audit logs into tamper-evident evidence bundles mapped to HIPAA, PCI-DSS, SOC 2 and GDPR.

Lets your AI find and run security tools for CTF, pentesting, bug bounty and DFIR work, under rules you set.

Your AI can sign a tamper-evident record of its decisions, so you can prove later what was decided and when.

Lets your AI check whether an action is allowed by your company's rules before it does it.

Let your AI check, harden, and keep an eye on your servers for you.

Adds a security checkpoint between your AI and its tools, so risky actions get blocked before they run.

Check a machine learning model file for unsafe or malicious code before you load or trust it.

Lets your AI register agents, check trust scores, verify credentials and rate other agents.

Lets your AI do network math, look up ports, check DNS, and inspect TLS certificates for you.

Give your AI signed permission slips and spending limits before it takes actions.

Gives your AI a safety rail: it can check whether an action is risky and keep a record of spending and human approvals.